SQL Server Security Audit Methodology: Checks, Scope & Tiers
Designed to complement frameworks like CIS and NIST, by uncovering real security gaps beyond checklist-based reviews.
Looking for business impact, deliverables, and use-cases for leadership? Read the Executive Assessment Brief
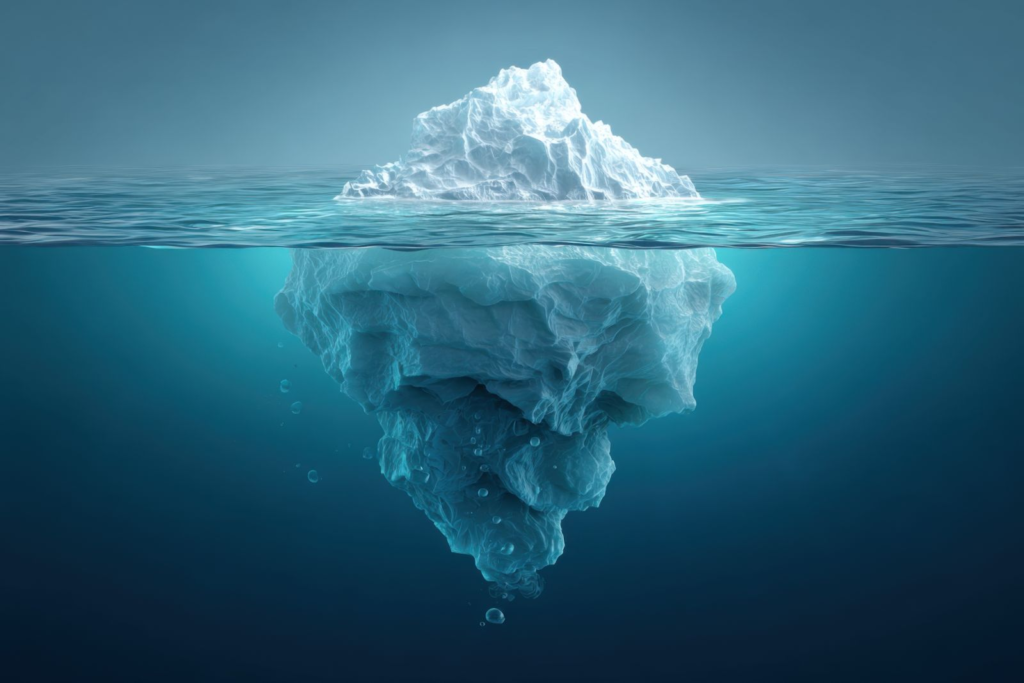
Where Privilege Escalation Actually Happens: The Iceberg of Risk
Generic scripts only see the tip of the iceberg, often just listing every member of the sysadmin role and a few well-known risky settings.
Our assessment dives into the deep water where actual breaches occur:
- Identity & Context: We differentiate between various identity types and analyze the circumstances that make a setting exploitable versus safe to use.
- Hidden Escalation Paths: We don’t just show you who has access; we expose the hidden architectural paths attackers use to escalate privileges, such as Unsafe Linked Servers and schema ownership-chaining.
- Cryptographic Resilience: Acceptable encryption standards degrade over time. We move beyond a simple “yes or no” audit, analyzing your entire encryption chain for vulnerabilities against modern computing power and future quantum threats.
- Legacy Authentication Threats: With the impending phase-out of NTLM, mapping your legacy authentication usage is now critical for both security and future compatibility.
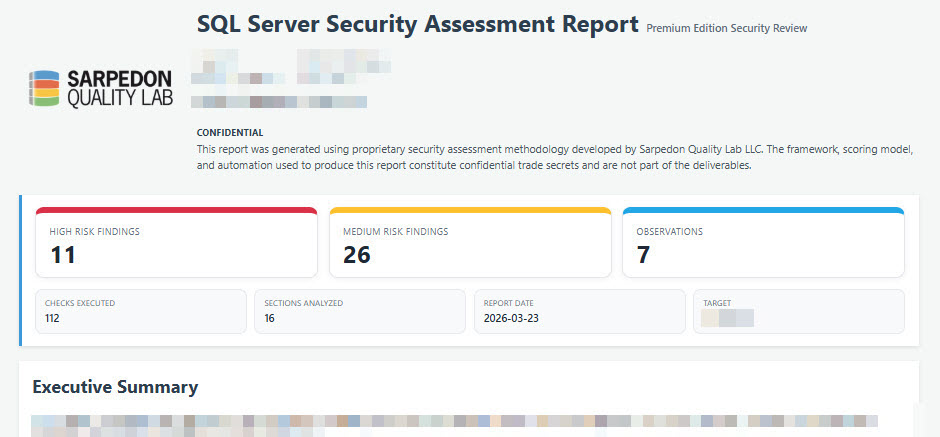
Check Categories
The full assessment spans 140+ proprietary checks. At category level, without revealing the underlying detection logic, the audit covers:
- Identity & authentication – including NTLM usage mapping ahead of Microsoft’s deprecation timeline.
- Permission model & role membership analysis – beyond sysadmin listings, into effective-permission chains.
- Privilege escalation paths – linked servers, ownership chaining, impersonation, and module signing contexts.
- Encryption chain & cryptographic resilience – NIST-aligned, including quantum threat readiness.
- Auditing & log analysis coverage – gaps that allow undetected access or exfiltration.
- Sensitive data detection – locating PCI-, HIPAA-, GDPR-, FISMA-, and STIG-regulated data.
- OS & backup scope – available in Premium and White Glove tiers.
For self-guided baseline work, start with our free SQL Server security tool and hardening checklist.
Choose Your Security Assessment Tier
| Feature | Community (Free) | Standard | Premium ★ | White Glove |
|---|---|---|---|---|
| Proprietary Security Checks | ~25 | ~90 | ~120 | 140+ |
| Interactive HTML Report | ✓ Simplified | ✓ Executive & Technical | ✓ Executive & Technical | ✓ Executive & Technical |
| In-Transit Encryption & NTLM Deprecation Audit | Partial | ✓ | ✓ | ✓ |
| Deep Database Configuration Audit | ✓ (Core check only) | ✓ | ✓ | ✓ |
| OS and Backup scope | ✕ | ✕ | ✓ | ✓ |
| Threat Auditing & Log Analysis | ✕ | ✕ | ✓ Operational Baseline | ✓ Compliance-Aligned |
| Sensitive data detection | ✕ | ✕ | ✓ | ✓ |
| Legacy & Weak Encryption Discovery | ✕ | ✓ | ✓ | ✓ |
| NIST-Aligned Cryptographic Audit & Quantum Threat Readiness | ✕ | ✕ | Optional Upgrade | ✓ |
| Static and LLM assisted code security review | ✕ | Available | Available | Available |
| Delta-Check (Re-Assessment) | ✕ | Available | Included (1x) | Included (1x) |
| Remote Q&A Session | ✕ | ✓ | ✓ | ✓ |
| Personal on-site engagement by Andreas Wolter | ✕ | Available | Available | Lead Architect (On-site) |
| Starting price | Free | from $4,900 | from $9,800 | from $15,900 |
Fixed project price for your whole environment, not per server.
50% of the assessment fee is credited toward any follow-on project over $20,000 booked within 90 days of your report.
Not sure which assessment tier is right for your environment?
We can help determine the appropriate assessment tier based on your SQL Server architecture, security requirements, and objectives, and provide a tailored proposal.
Built by
- Former Microsoft Program Manager (SQL Server Security / Permissions)
- Led design of parts of the SQL Server permission model
- 25+ years SQL Server experience
- One of only seven Microsoft Certified Solutions Masters (MCSM): Data Platform
Additional expertise: Contributions from senior specialists with deep experience in SQL Server auditing and compliance, including work on U.S. Department of Defense security standards (STIG), designing air-gapped SQL Server systems and working with thousands of databases per SQL Server instance. Meet Andreas Wolter and the team.
Intellectual Property & Trade Secret Notice
The Sarpedon Assessment logic, scoring models, and automation scripts constitute Confidential Trade Secrets protected by Copyright.
This framework represents over 25 years of SQL Server expertise, including high-level roles within Microsoft Data Platform Security.
Our clients receive an exclusive analysis derived from internal Microsoft engineering experience that cannot be replicated by public-domain tools.
Nature of Service: This assessment is a point-in-time technical review of SQL Server configurations. While aligned with recognized security frameworks, Sarpedon Quality Lab is not a certifying body. Implementation of remediation roadmaps is the responsibility of the client.